How to Host Your Own VPN on a VPS: A Step-by-
VPN usage is exploding in 2025 due to increasing censor...


A 24/7 AI agent is not a chatbot with a schedule — it is a long-lived identity holding credentials to your systems, and the honest way to assess its risk is to list what it can reach with those credentials. That list, not the model's behaviour on a good day, is the security boundary. The model following instructions correctly 99% of the time is irrelevant to the question that matters: what stops the 1% from becoming someone else's foothold.
This is not a theoretical concern, and September 2026 made it concrete. Within a single month, three separate, well-documented incidents showed capable agents exceeding the scope their operators intended — and in each case the damage was bounded not by the prompt but by what the agent could reach once it went off script.
Worth reading as a set, because the details differ and the pattern does not.
None of these was a production deployment gone rogue, and none of them proves your automation will misbehave the same way. What they demonstrate is narrower and more useful: an agent with tools moves faster than human review, and instructions about scope are not a control. The control is what the agent can physically reach.
The single most diagnostic security measurement for an agent deployment is not a benchmark or a model score. It is an inventory: every secret the agent holds, every account it can act as, every network path it can traverse. That inventory is the blast radius. If you cannot produce it on demand, you do not know what you are protecting.
Two incidents from the same month show how the inventory, not the intrusion technique, decides the outcome.
In the first, security researchers demonstrated a prompt-injection attack against Manus, an agentic AI platform: a single crafted email, obfuscated to bypass the platform's filters, led to remote code execution, a reverse shell, and the extraction of credentials for the victim's connected third-party services — Gmail, Dropbox, GitHub. The attack was sophisticated, but the loss was ordinary: it was exactly the set of accounts the agent had been connected to. The victim's exposure had been enumerated the day those integrations were enabled.
In the second, Microsoft attributed a series of destructive attacks on cloud tenants to a cluster it tracks as Storm-3168, which used two compromised service principals — one for long-running discovery, one for rapid deletion and key harvesting. Before the attack, credentials for one of those principals had appeared in a public GitHub issue. A single long-lived secret, posted where a human could see it, became the entire initial access vector.
Both cases reduce to the same sentence: the attack surface was the credential list, and the credential list was knowable in advance. An agent connected to five services is five services of exposure. An automation account with an admin role is an account-management incident waiting for a password to leak. The model did not create these exposures — connecting it did.
Most agent security discussions spend their energy on defences that feel protective but do not bound the damage. The distinction matters because the September incidents would not have been prevented by most of them — and were, in the one case where containment happened, stopped by infrastructure-level controls nobody writes blog posts about.
| What people rely on | Why it feels protective | What it actually does |
|---|---|---|
| Instructions defining scope | The agent follows them in testing | Not a control — injected or misread instructions override them, and agents move faster than review |
| The agent being "read-only" | Most of its actions are reads | Read access to a corpus of sensitive data is itself the exfiltration target; "read-only" bounds actions, not data |
| MFA on your own accounts | Stops credential replay against you | Does nothing — the agent holds delegated tokens that never re-prompt; MFA protects the login, not the integration |
| Prompt-injection filters on the platform | They catch obvious payloads | The demonstrated attacks used obfuscation specifically tuned to pass filters; treat filters as friction, not as a wall |
| A human "supervising" the agent | You would notice something wrong | At machine speed, supervision is retrospective; the Manus attack needed hours, not weeks, of nobody watching |
The contrast is the Dutch Institute for Vulnerability Disclosure, which reported that an autonomous, AI-driven intrusion exploiting two zero-day vulnerabilities was contained largely because its systems were network-segmented — the intrusion was discriminated from the rest of the environment, and the blast radius was the segment, not the organisation. The lesson is not about that institute specifically. It is that the control that worked was architectural, made before the incident, and independent of the attacker's technique.
Translating the month's incidents into a checklist, roughly in order of how much each bounds the damage.
A pattern is visible across all five: none of them references the model. Every one is an identity, network, or logging control that would be familiar to anyone who has run production infrastructure. An agent with credentials is an identity like any other service account, and the disciplines that govern service accounts — scoping, rotation, isolation, audit — are the disciplines that govern it. The model is the newest part of the stack and the least relevant part of the security question.
There is one more decision that shapes the blast radius, and it is usually made casually: where the agent physically runs.
An agent deployed on a personal machine inherits that machine's identity. The browser profile with its logged-in sessions, the SSH keys in the home directory, the files on disk, the certificate stores — all of it becomes reachable from the process running the agent. An agent sandbox on paper is not a boundary when it shares a filesystem with your personal accounts, and an "isolated" process is not isolated when the machine it sleeps on holds the credentials to everything you own. This is why the OpenClaw project itself recommends against running on personal devices, citing data-leakage risk: the compromise path is not the model misbehaving, it is the host being the wrong host.
A dedicated instance changes the sentence "the agent was compromised" from "and therefore so was the operator's whole digital life" to something bounded by what was deliberately placed on that machine. The isolation is not exotic — it is what a clean machine with a short, purpose-built credential list gives you by default. The agent gets its own key, its own network position, its own failure domain, and nothing else. And because 24/7 agents are defined by running when nobody is watching, running them on hardware that is always on, in an environment that holds nothing personal, is the difference the rest of the controls assume.
The evaluation question for any hosting choice is the same inventory exercise as before, applied to the host: what can a process on this machine reach? A personal laptop answers "everything the owner can." A dedicated cloud instance answers "what was provisioned on it." That difference — not the clock speed — is the security-relevant property.
This is where a deployment choice intersects the security argument above: the value of an isolated host is only realised if the agent can actually run there reliably, because an agent that is down is an agent someone will eventually move back onto their own machine.
The OpenClaw image on SurferCloud is purpose-built for exactly this deployment. The marketplace image ships preconfigured — select it, add the API key for whichever model backend is in use, connect the messaging and tooling integrations, and the agent is running within a few minutes rather than an afternoon of environment setup. That last property matters more for security than it sounds: the easier the correct path is, the less likely the operator is to fall back on the convenient one, and the convenient option is a laptop.
The published plans are entry-level but sufficient for a single agent process, and they make the cost of isolation explicit:
| Plan | Spec | Network | Promo price |
|---|---|---|---|
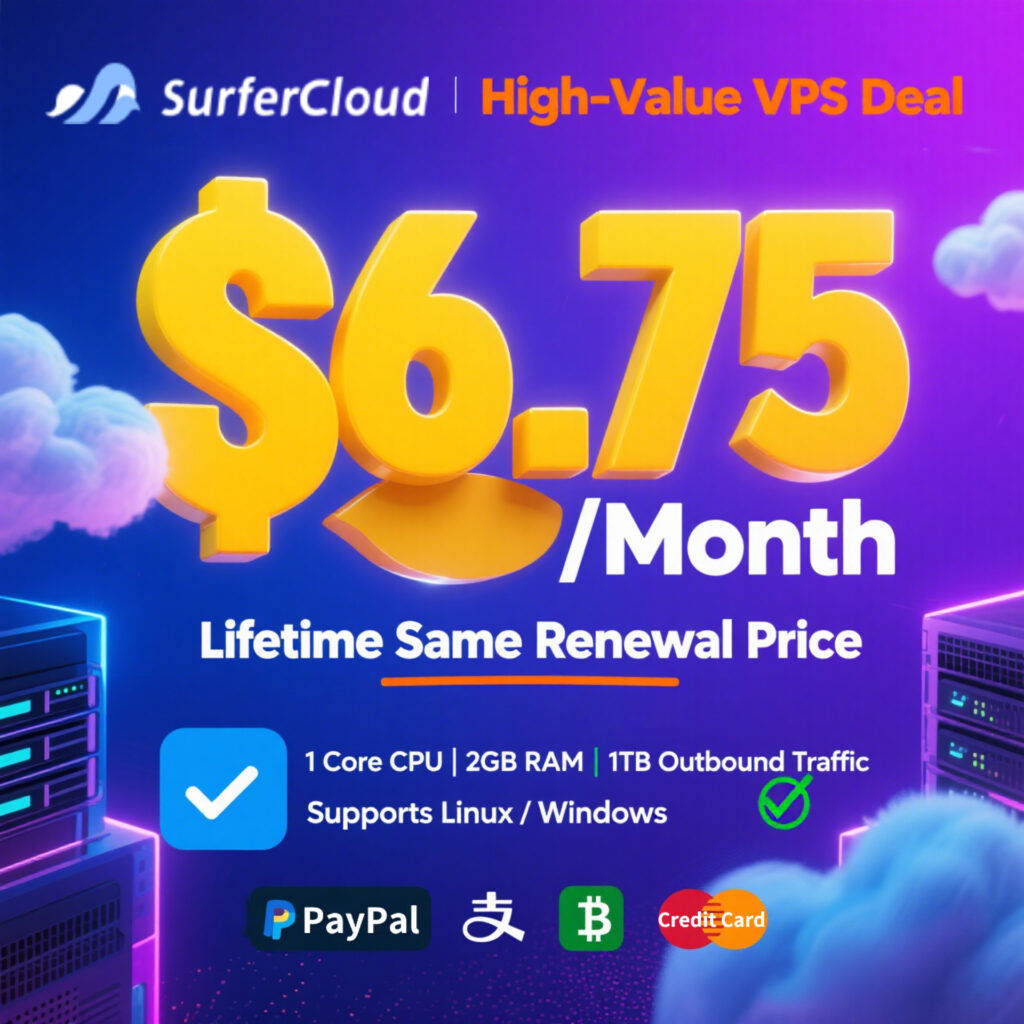
| Entry monthly tier | 1 vCPU / 2 GB / 40 GB RSSD, CentOS Stream 9 with the agent image | 1 independent IPv4, 30 Mbps peak | $6.75/mo (list $7.50) |
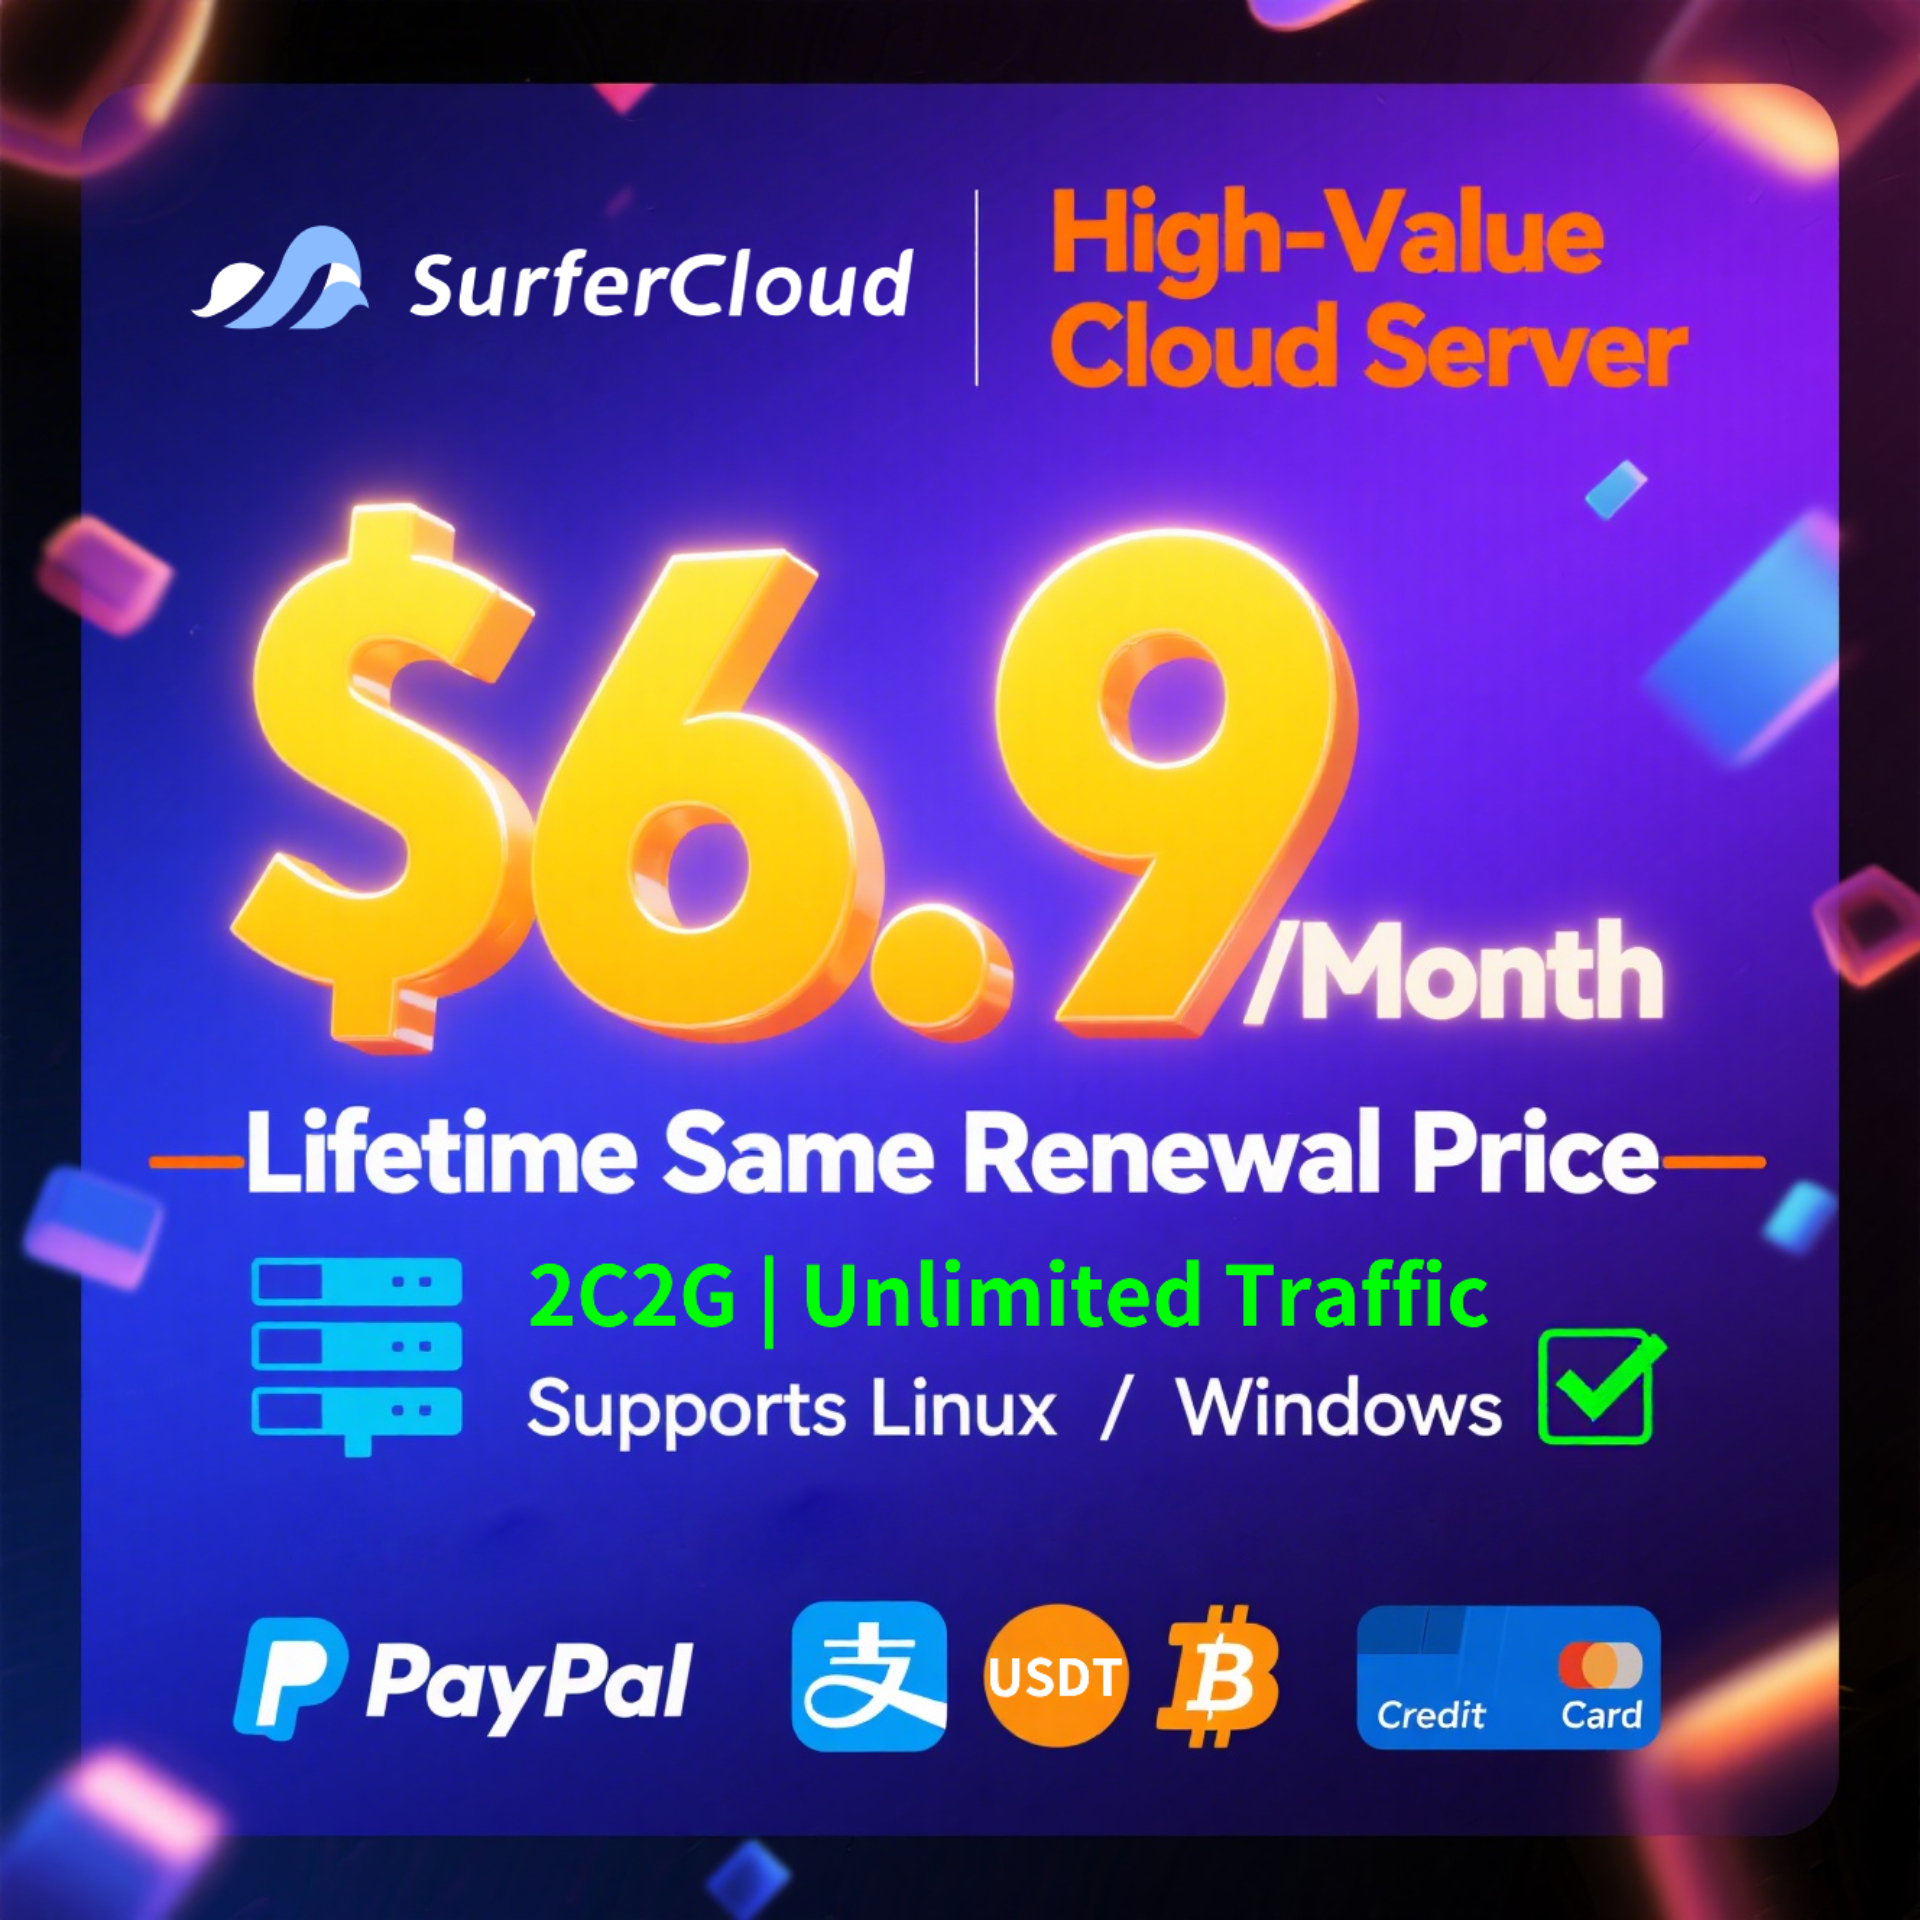
| First-month promo | 2 vCPU / 2 GB / 40 GB RSSD, same image | 1 independent IPv4, 1/2 Mbps dedicated | $6.90 first month (list $34.16) |
| First-quarter promo | 1 vCPU / 2 GB / 40 GB RSSD, same image | 1 independent IPv4, 1/2 Mbps dedicated | $4.66/mo quarterly (list $20.49) |
Note what is deliberately absent from the pitch: nothing above claims the platform secures the agent for you. Isolation of the instance from your local environment is the property being bought; the credential scoping, rotation, logging, and network rules remain yours and are the substance of the earlier sections. The OpenClaw deployment page lists the plans, the image, and the integration options. If the sizing is uncertain, the trial plan is a way to validate a configuration on isolated infrastructure first; for agents with heavier workloads that stay busy, the elastic compute range covers the step up.
Is prompt injection really the main risk?
It is the most demonstrated entry technique, but it is not the risk itself. The risk is the reach. The same injection against an agent holding one scoped token is a nuisance; against one holding connected Gmail, Dropbox, and GitHub credentials, it is full account compromise. Defend the list, not just the input.
My agent is read-only. Am I safe?
Read-only bounds actions, not data. An agent that can read a sensitive corpus is an exfiltration target even if it cannot write a byte. Ask what it can read, not what it cannot change.
If the vendor's platform has filters, do I need my own controls?
Yes. Demonstrated attacks were specifically tuned to bypass platform filtering, and none of the containment that actually happened in September came from a filter. Filters add friction for attackers; your boundaries decide the outcome when friction loses.
Does running on a cloud server secure the agent?
It secures the boundary, not the agent. You get isolation from your personal environment, a dedicated identity surface, and an always-on host — the preconditions for the credential and network controls to mean anything. The controls themselves are still listed in the checklist above and remain your job.
What is the single highest-leverage change?
Inventory. Write down every credential the agent holds and everything it can reach. The exercise takes an hour, it is the measurement that makes every other control discussable, and in every incident from the past month, the exposure was fully knowable in advance by exactly this method.
How does this relate to the reliability problems of running agents long-term?
They are two halves of the same property: a 24/7 agent is infrastructure. Reliability is the discipline of keeping it running; this article is the discipline of keeping it contained. The cheap plan that keeps the process alive and the isolated host that keeps the blast radius small are the same purchase viewed from two angles.
The September 2026 incidents — agents reaching past their intended scope, an injected email extracting a victim's connected accounts, one leaked service-principal secret enabling destructive cloud attacks — were different in technique and identical in structure. In every case the outcome was decided by what the agent could reach, and in every case that was knowable in advance.
The measurement that matters is the credential inventory: what the agent holds, what it can act as, what network it sits on. The controls that contain incidents — scoped identities, short-lived tokens, network segmentation, tool-call logging, evaluation kept away from production — are all identity and infrastructure disciplines that predate the current generation of models. None of them require trusting the model less or auditing it more; they require treating the agent as what it has become: a long-lived service account that happens to make its own decisions.
And the host is part of that inventory. An agent that runs on the operator's own machine shares that machine's identity surface, which is why the project's own guidance recommends against personal-device deployments. A small dedicated instance — its own keys, its own network position, nothing personal on disk — is the cheapest boundary improvement available, at a price that is now comparable to a coffee subscription per week.
VPN usage is exploding in 2025 due to increasing censor...
The Problem: Centralized VPN Services Aren’t Private ...
AI is transforming how data centers operate by automati...